Shadow AI: Your Employees Are Already Using AI Without You Knowing (and Leaking Data)
Summary, Core Thesis, Key Insights and Strategic Recommendations Summary While boards of directors debate "AI security" in closed meetings, the reality on the ground is different: employees have already massively adopted public tools to increase productivity, often exposing confidential data. This article defines the Shadow AI phenomenon, explains why firewall blocking policies are ineffective and proposes the creation of AI "Safe Harbors" as the only viable mitigation strategy. [...]
16 de abril de 2026
Summary, Core Thesis, Key Insights and Strategic Recommendations
Summary
While boards of directors debate “AI security” in closed meetings, the reality on the ground is different: employees have already massively adopted public tools to increase productivity, often exposing confidential data. This article defines the Shadow AI phenomenon, explains why firewall blocking policies are ineffective and proposes the creation of AI “Safe Harbors” as the only viable mitigation strategy.
Core Thesis: The greatest information security risk today is not the implementation of corporate AI, but the absence of it. By not providing official and governed tools, companies push their employees toward clandestine use of public LLMs (Shadow AI), where intellectual property can be used as training data for third-party models*.
Key Insights:
- The Productivity Dilemma: The employee doesn’t use ChatGPT to harm the company; they use it because they need to deliver the report by 5 PM and the official tool is slow or nonexistent.
- Blocking is an Illusion: Banning access to OpenAI on the corporate network only makes employees use 4G on their personal phones, where the company has zero visibility.
- Invisible Leak: Sensitive data (source code, M&A strategies, customer data) is being pasted into public chats, becoming part of the global model’s knowledge.
Strategic Recommendations:
- Replace the “Prohibition” policy with a “Substitution” policy: Offer a secure and monitored Corporate Chat (Enterprise Instance).
- Implement DLP (Data Loss Prevention) filters specific to prompts, detecting patterns of SSN or credit card numbers before sending to the API.
- Run awareness campaigns on how public LLMs retain data.
Context and Business Problem
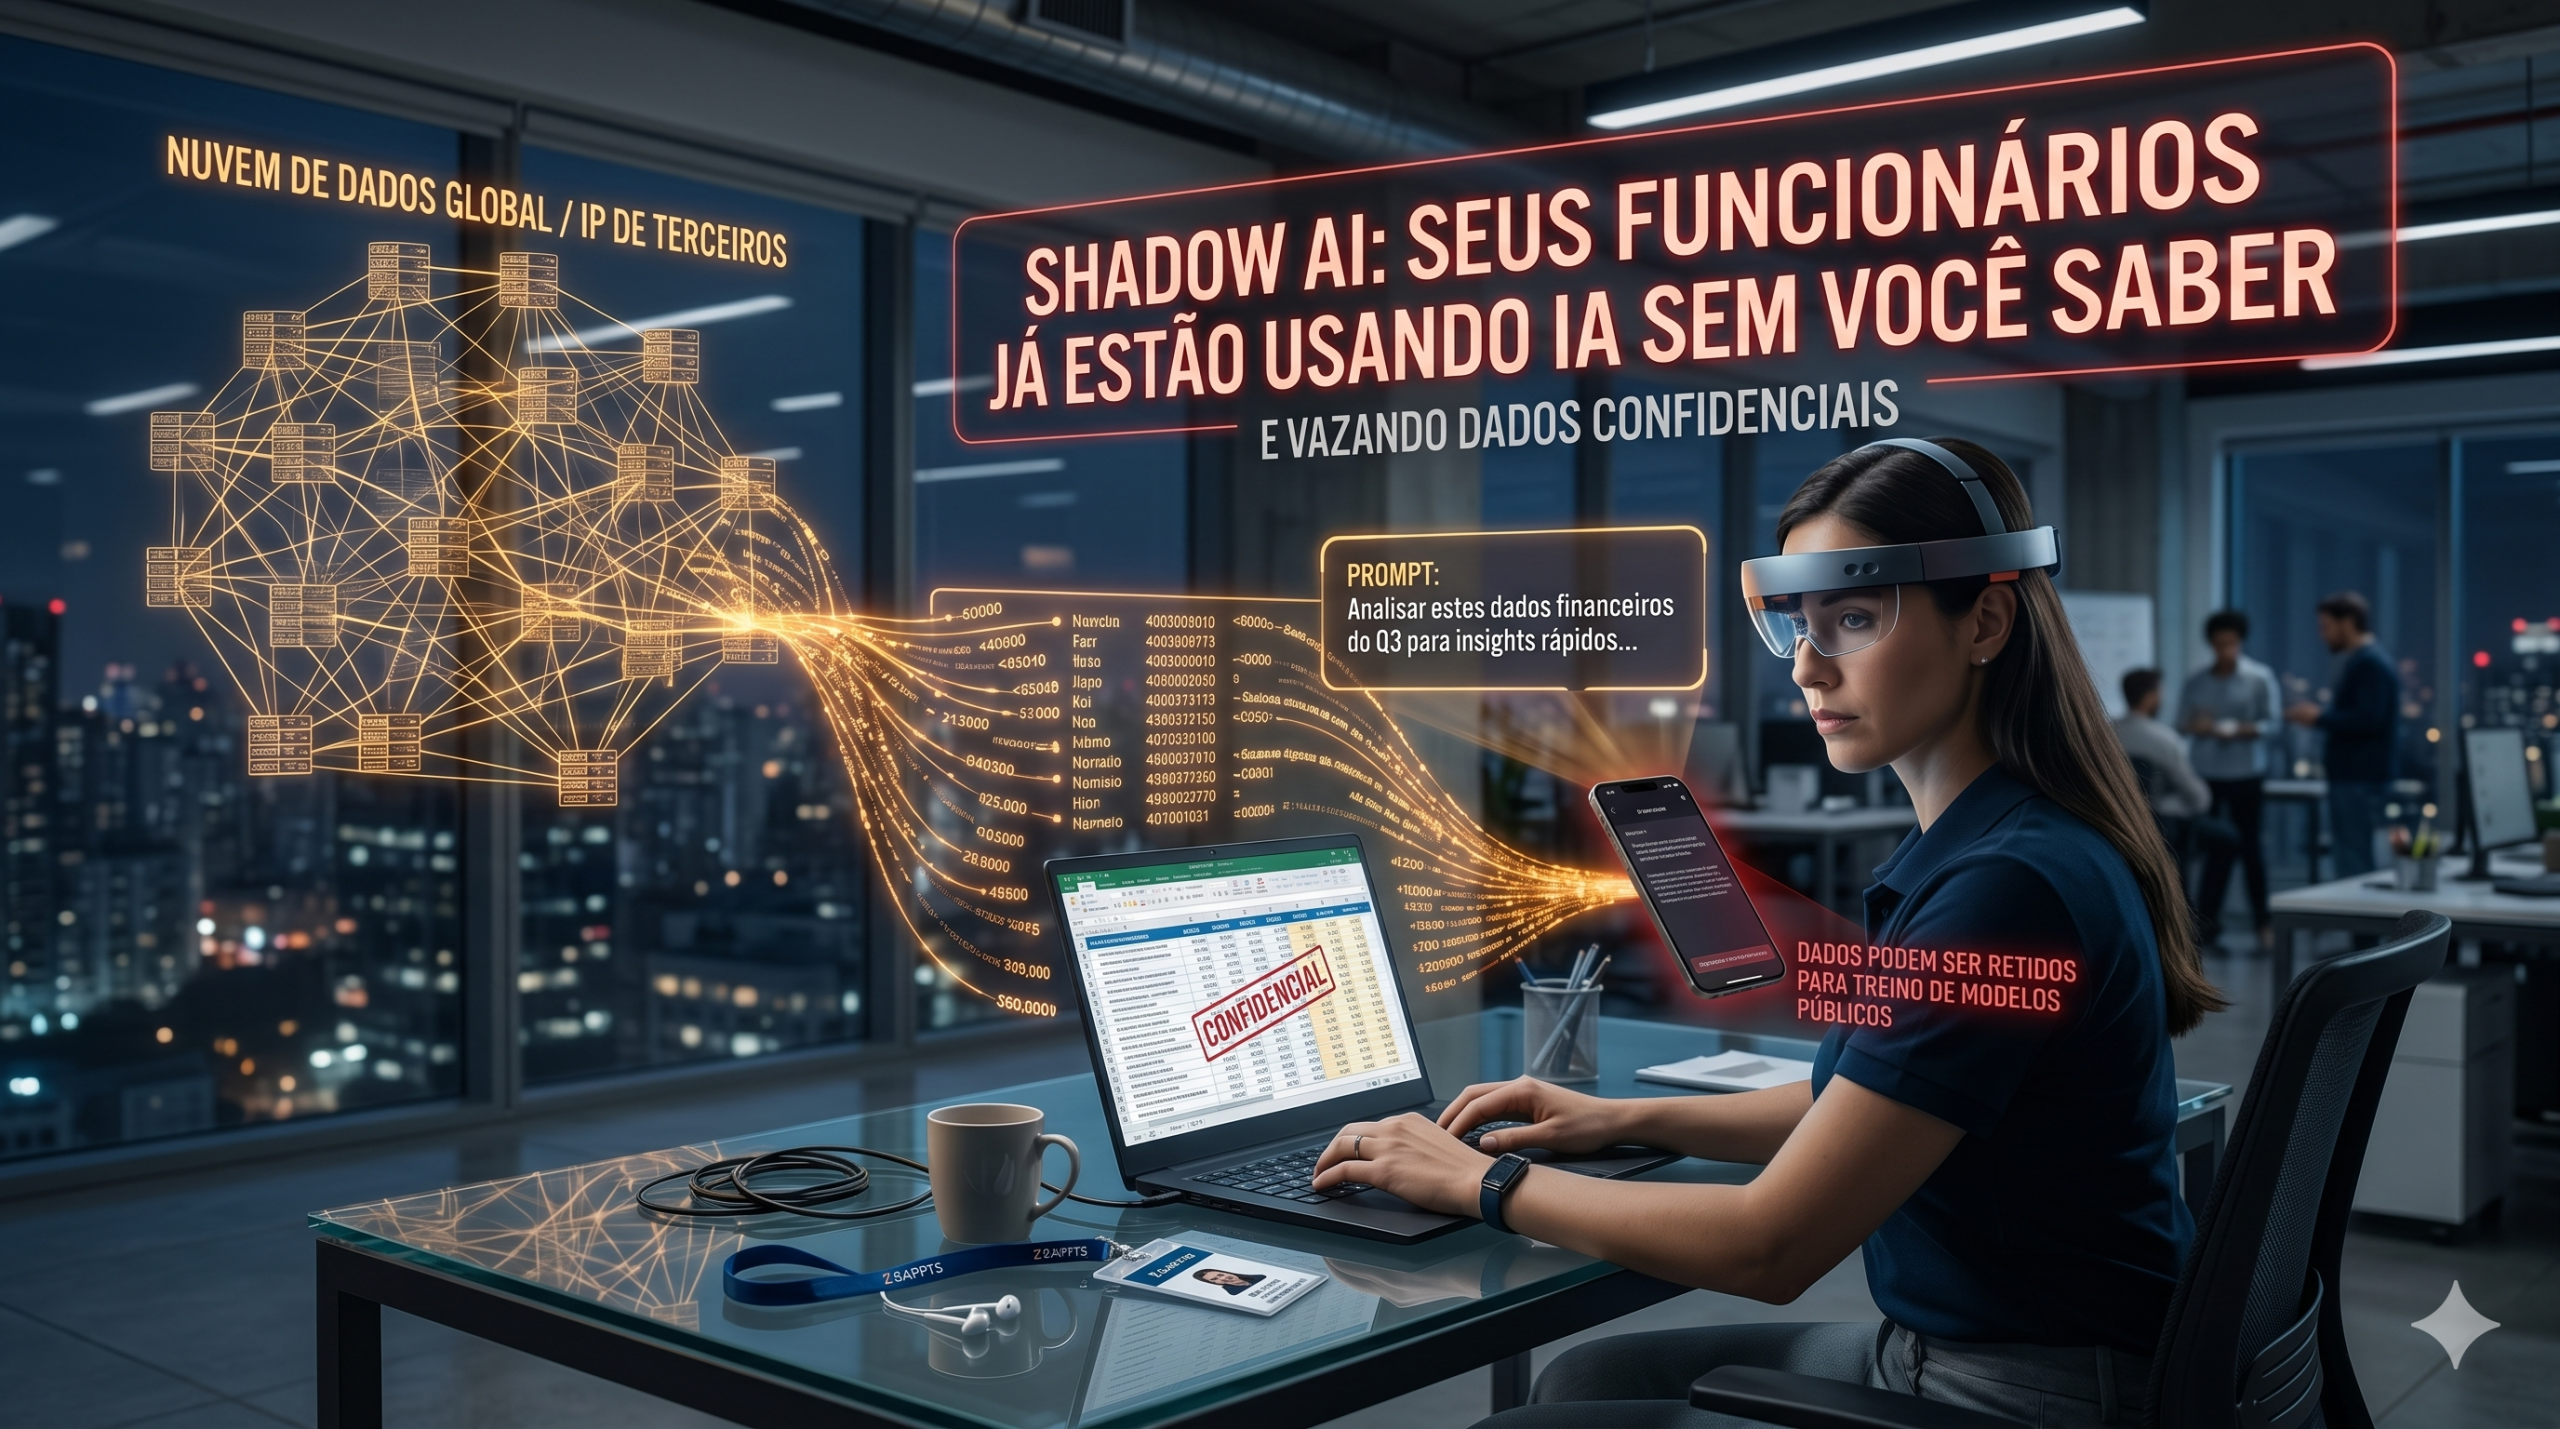
Imagine the following scenario: A financial analyst receives a complex spreadsheet with billing data from last quarter. The deadline is tight. They know that if they ask the Data team, it will take 3 days. They also know that if they paste this data into ChatGPT, they’ll have the analysis in 30 seconds. What do they do? They paste.
At that moment, your company’s financial data left the security perimeter and was sent to public servers, where it can be retained for future training.
This is Shadow AI. It is the decentralized, invisible and unregulated adoption of Artificial Intelligence tools by well-intentioned employees. According to market studies and evidence from our study AI Panorama in Brazil, the discrepancy between “official adoption” (what IT approved) and “real adoption” (what people use) is alarming.
Market Drivers: The Inevitability of Use
Why is Shadow AI so prevalent?
- Radical Accessibility: Anyone with a personal email can access the most powerful AI models in the world for free. The barrier to entry is zero.
- Pressure for Efficiency: In a market that demands “doing more with less”, employees see AI as the only lifeline to keep from drowning in tasks.
- IT Slowness: While IT takes 6 months to approve a tool (POCs, RFPs, Compliance), the market changes. The employee doesn’t want to wait.
Strategic Analysis: From Ostrich to Safe Harbor
There are two ways to deal with Shadow AI:
- The Ostrich Strategy (Ineffective): The company pretends it isn’t happening or tries to block URLs on the firewall.
- Result: Usage migrates to personal devices (or BYOD – Bring Your Own Device), becoming completely unauditable. The risk increases.
- The Safe Harbor Strategy (Recommended by Zappts): The company recognizes the demand and offers an official alternative.
- Action: “We know you want to use AI. Here is the Enterprise Chat, which uses the same model you like, but runs in a private environment where your data is not used for training and we have audit logs.”
When you offer a better and safer tool than the public one, Shadow AI naturally disappears. No one uses the pirated tool if the official one is good.
Implications for Organizations
Ignoring Shadow AI has legal and strategic consequences:
- LGPD Violation: If an employee pastes customer data into a public AI that suffers a data breach, the responsibility lies with the controlling company.
- IP Loss (Intellectual Property): Proprietary code pasted into public coding assistants may appear as suggestions for developers at competing companies in the future.
Strategic Recommendations
For CTOs, CISOs and DPOs:
- Launch an Internal Chat MVP in 30 Days: Don’t try to build the “perfect AI” now. Just make a secure interface available (like Azure OpenAI or Amazon Bedrock) to get your users off public ChatGPT. Zappts can help you with this challenge.
- Classify Your Data: Make clear what can and cannot go into AI. “Public Data: OK. Internal Data: OK in Corporate Chat. Confidential Data: Prohibited.”
- Prompt Auditing: In the corporate environment, keep logs of what is asked. This is not to monitor employees, but to identify process bottlenecks and security risks (e.g., someone trying to unlock jailbreaks).
- Educate, Don’t Just Punish: Show teams how LLMs work. Most people don’t know the free chat uses their data*.
Conclusion
Cybersecurity in the AI era is not built with walls, but with paved roads. If you don’t build the safe road for innovation, your employees will cut shortcuts through the woods. And in the woods, your data is unprotected. Take control of Shadow AI by bringing it into the light of governance.
Bonus: How your data is legally treated when using Public or Private AI Chats.
This is how your shared data is treated in AI Chats: in public versions (free or individual plans), the content of interactions may be treated as input for AI improvement, being incorporated into training databases for future model iterations. In contrast, in private or corporate versions (Enterprise, Business and API plans), platforms offer contractual privacy guarantees, ensuring that provided information remains isolated and is never used to train global models or shared with other users, thus protecting intellectual property and sensitive data confidentiality.
About the Author
Rodrigo Bornholdt is Co-founder and Chief Technology Officer at Zappts, specialized in Software Architecture and Artificial Intelligence, with solid experience in technology team leadership, complex systems development, and innovation applied to business strategies.
About Zappts
With 12 years of experience, Zappts is a technology and innovation company that is a reference in Agentic Transformation for large corporations. The company has accumulated over 280 projects executed and 1 million engineering hours for sectors such as finance, healthcare, retail and energy. It is the creator of the AI Panorama in Brazil, a survey that maps national technological maturity, and a reference in implementing AI agents integrated with core business focusing on governance, ROI and operational efficiency. Click here to learn more.
Share this article
Related articles
16 set 2026
The End of Passive SaaS: Why You’ll Pay for Outcomes, Not Seats
The traditional software pricing model based on per-user licenses (seat-based SaaS) faces an inevitable decline in 2026.
09 set 2026
The Timid Autonomy Dilemma: Why Keeping AI in a Suggestion-Only Role Is Killing Your Margins
This article analyzes the financial impact of this "timid autonomy" and advocates for an urgent shift to the "Human-on-the-loop" (HOTL) model.
02 set 2026
The "SaaSocalypse" is actually an architecture and identity crisis.
This article reverse-engineers a real-world success story (anonymized) from the financial sector, dissecting the layers of...